Reliability by Design
Service objectives, redundancy, recovery testing, capacity policies, and failure-mode reviews shape resilient platforms.
We plan, architect, and execute enterprise cloud transformation strategies — migrating legacy infrastructure to AWS, Azure, and Google Cloud while optimizing performance, security, and cloud expenditure.
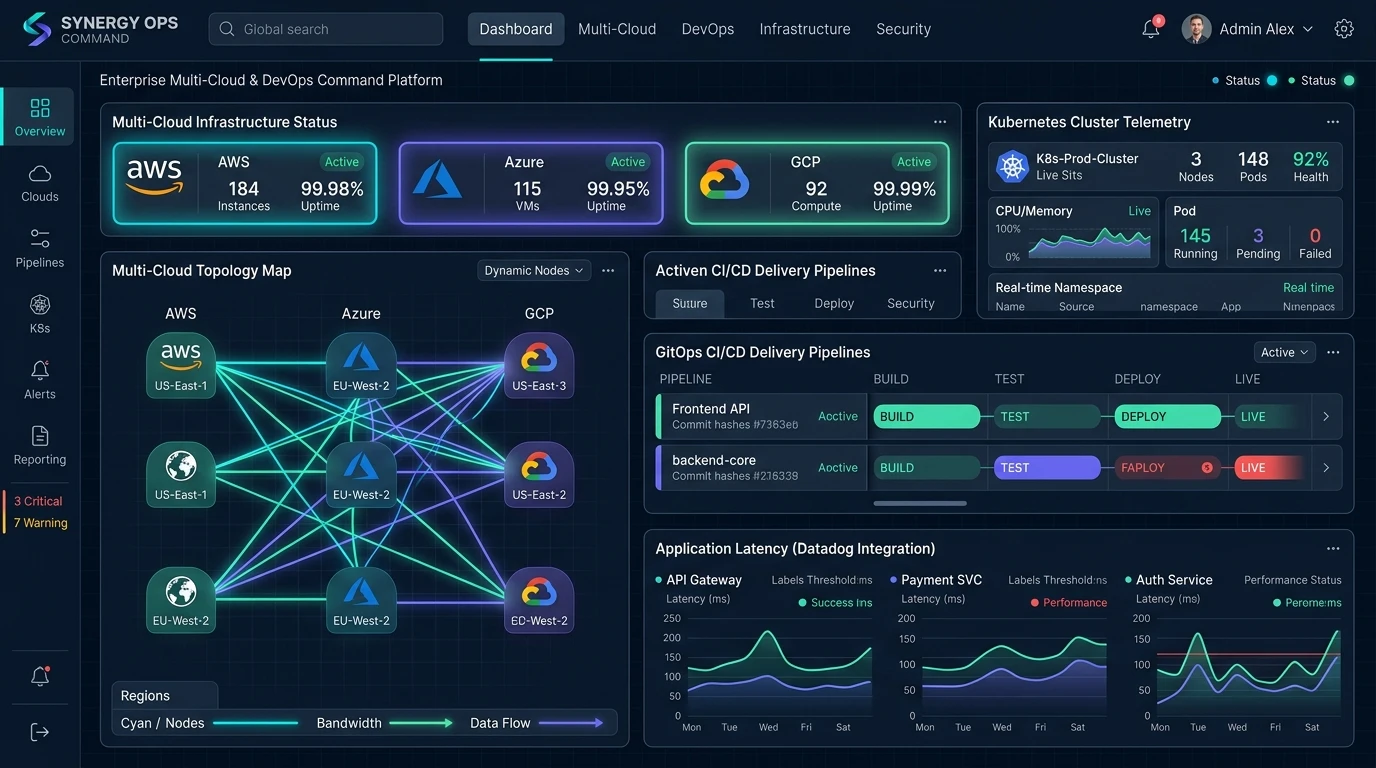
Six enterprise cloud engineering pillars built to scale application infrastructure, automate deployment pipelines, and reduce cloud expenditure.
Continuity-focused database replication, automated workload migration, multi-region networking, and hybrid cloud gateway architecture.
Production-grade Kubernetes clusters, automated Horizontal Pod Autoscaling (HPA), Istio service mesh, and container security scanning.
Automated software delivery pipelines with progressive blue/green deployments, unit and integration test suites, and rollback triggers.
Modular, version-controlled Terraform infrastructure templates supporting consistent cloud environments across staging and production.
Automated container image vulnerability scanning, AWS IAM least-privilege security policies, secrets vault management, and SOC2 audit compliance logging.
Real-time Datadog/Grafana telemetry, spot instance scheduling, unattached volume purging, and automated monthly cloud bill reduction strategies.
Reduce manual configuration bottlenecks with automated Terraform blueprints, progressive blue/green delivery pipelines, and container orchestration with tested rollback controls.
Version-control your entire cloud environment in Git code repositories, allowing instant 1-click environment spinning.
Shift traffic gradually, validate application health, and roll back safely when release signals fall outside agreed thresholds.
Automatically spin up microservice pods during traffic spikes and scale down during off-peak hours.
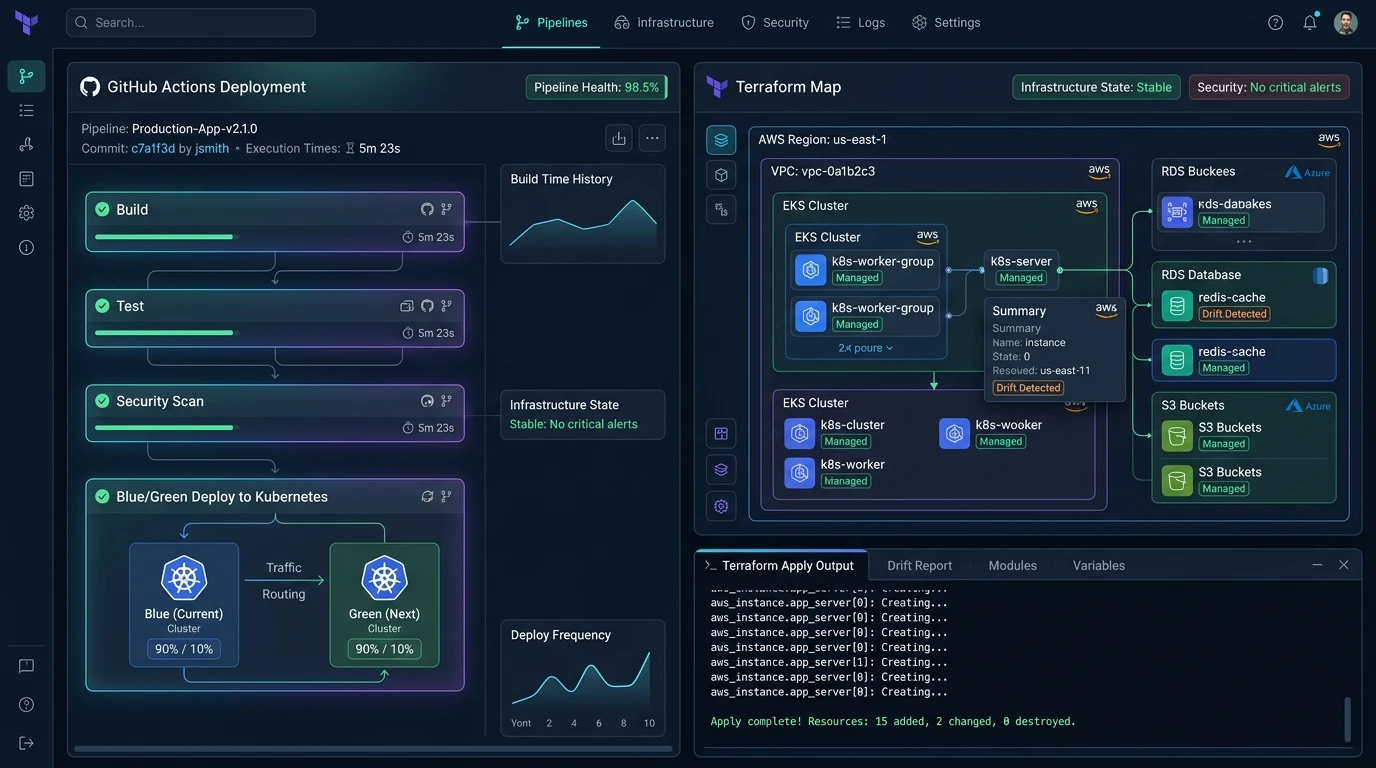 Versioned infrastructure and controlled delivery
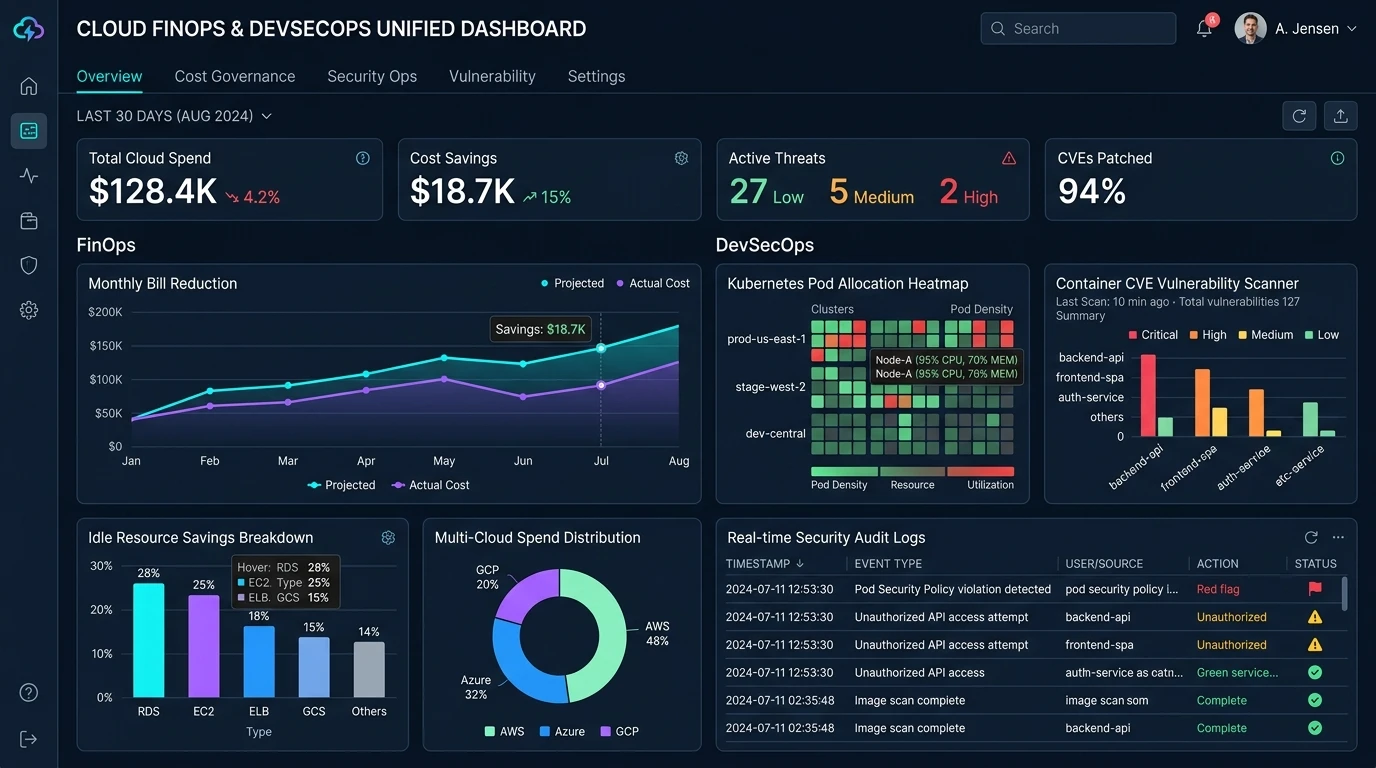 Security and cost signals inside daily operations
Embed vulnerability checks into delivery pipelines while continuously measuring utilization, ownership, and cloud spending to identify practical optimization opportunities.
Identify unattached disk volumes, over-provisioned EC2 instances, and schedule non-production server sleep cycles.
Scan Docker images and npm/composer dependencies for CVE vulnerabilities automatically before merging to main.
Prevent API token leaks using HashiCorp Vault and AWS Secrets Manager encrypted token storage.
From AWS/Azure enterprise multi-cloud migrations and Kubernetes microservices clusters to CI/CD delivery automation, serverless APIs, and FinOps cost optimizations.
Migrating physical data centers to cloud networks with phased cutover planning, validation, and multi-region resilience.
Elastic EKS/AKS cluster setup with Istio service mesh, Prometheus monitoring, and automated pod scaling.
GitHub Actions and GitLab CI/CD pipelines executing automated tests, Docker container builds, and deployment.
Comprehensive cloud infrastructure audit identifying over-provisioned resources to slash monthly AWS/Azure bills.
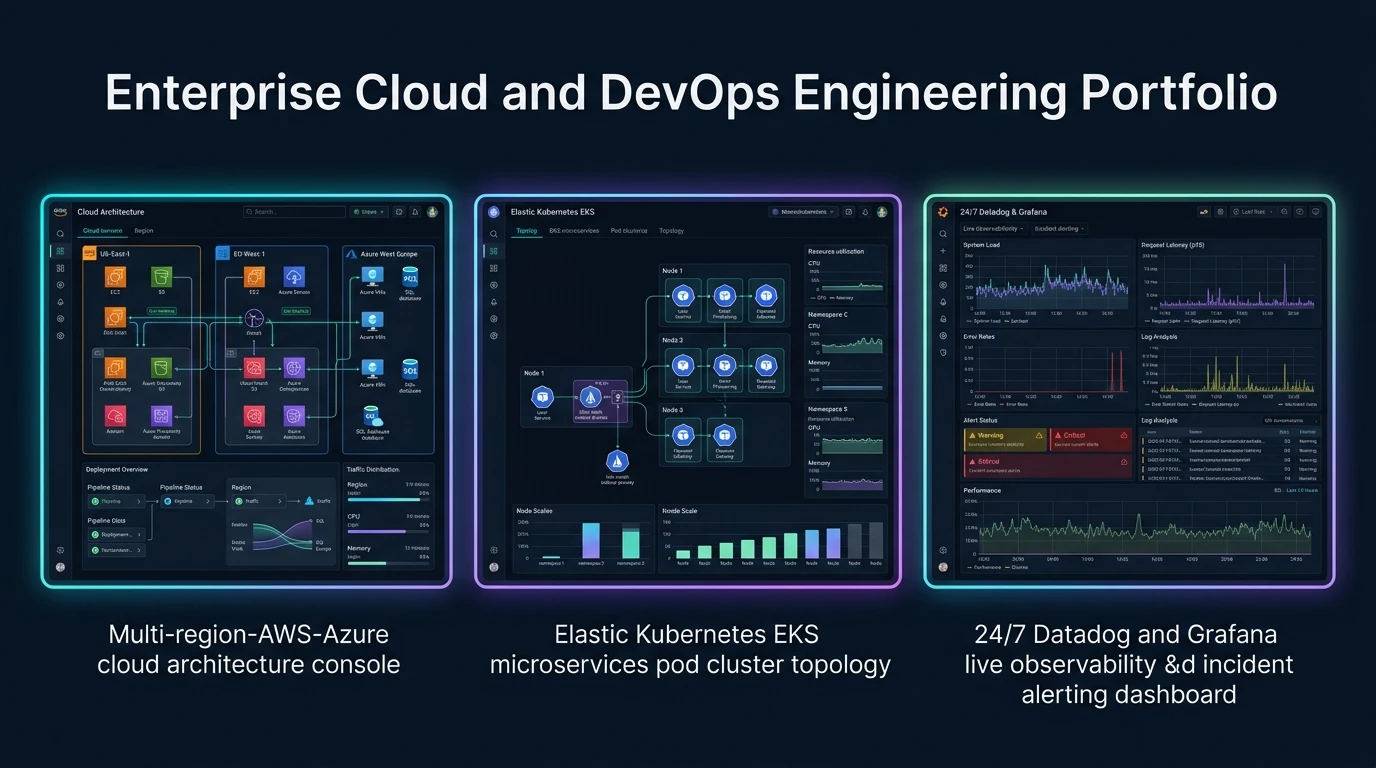 Platforms built around real operating requirements
Our disciplined cloud engineering process reduces migration risk, protects data integrity, and establishes measurable reliability controls.
Auditing current server topologies, database bottlenecks, security compliance risks, and monthly hosting costs.
Writing modular Terraform HCL templates for VPC networks, Kubernetes clusters, database replicas, and IAM security.
Engineering automated GitHub Actions or GitLab CI/CD pipelines with automated test suites and blue/green deployments.
Dockerizing application services and configuring Kubernetes pod auto-scaling, ingress controllers, and SSL certificates.
Data replication, validation, progressive traffic routing, and rehearsed rollback procedures for a controlled launch.
Setting up 24/7 Datadog/Grafana alerts, automated disaster recovery backups, and monthly cloud bill optimization.
We build using tier-one enterprise cloud providers, container orchestration tools, and automated deployment systems.
Enterprise Multi-Cloud Infrastructure
Version-Controlled Infrastructure as Code
Container Auto-Scaling & Orchestration
Progressive Continuous Delivery
See how automated cloud & DevOps engineering compares to slow, manual server hosting.
Everything you need to know about custom cloud & DevOps engineering with Sibiri Innovation.
We select continuity controls based on the workload, including replication, staging synchronization, phased traffic routing, maintenance-window planning where required, reconciliation checks, and tested rollback procedures.
We audit tagging, utilization, storage, compute sizing, scheduling, commitment options, and workload architecture. Savings depend on the existing environment and are validated against an agreed cost baseline.
Yes. Every enterprise service page includes an integrated admin control panel allowing authorized team members to update headings, paragraphs, section images, key metrics, and SEO metadata dynamically.
A standard cloud migration and DevOps automation build takes 4 to 8 weeks, including architecture audit, Terraform IaC blueprinting, CI/CD pipeline setup, Kubernetes containerization, and zero-downtime cutover.